Know what's exposedbefore it's exploited.
Search leaked credentials, stealer logs, dark-web posts, and raw breach files from one console. Every result stays masked until you reveal it, and you pay only for what you reveal.
Free exposure check for an address you own. Or create a free account.
- No card required
- Masked by default
- Cost shown before every reveal
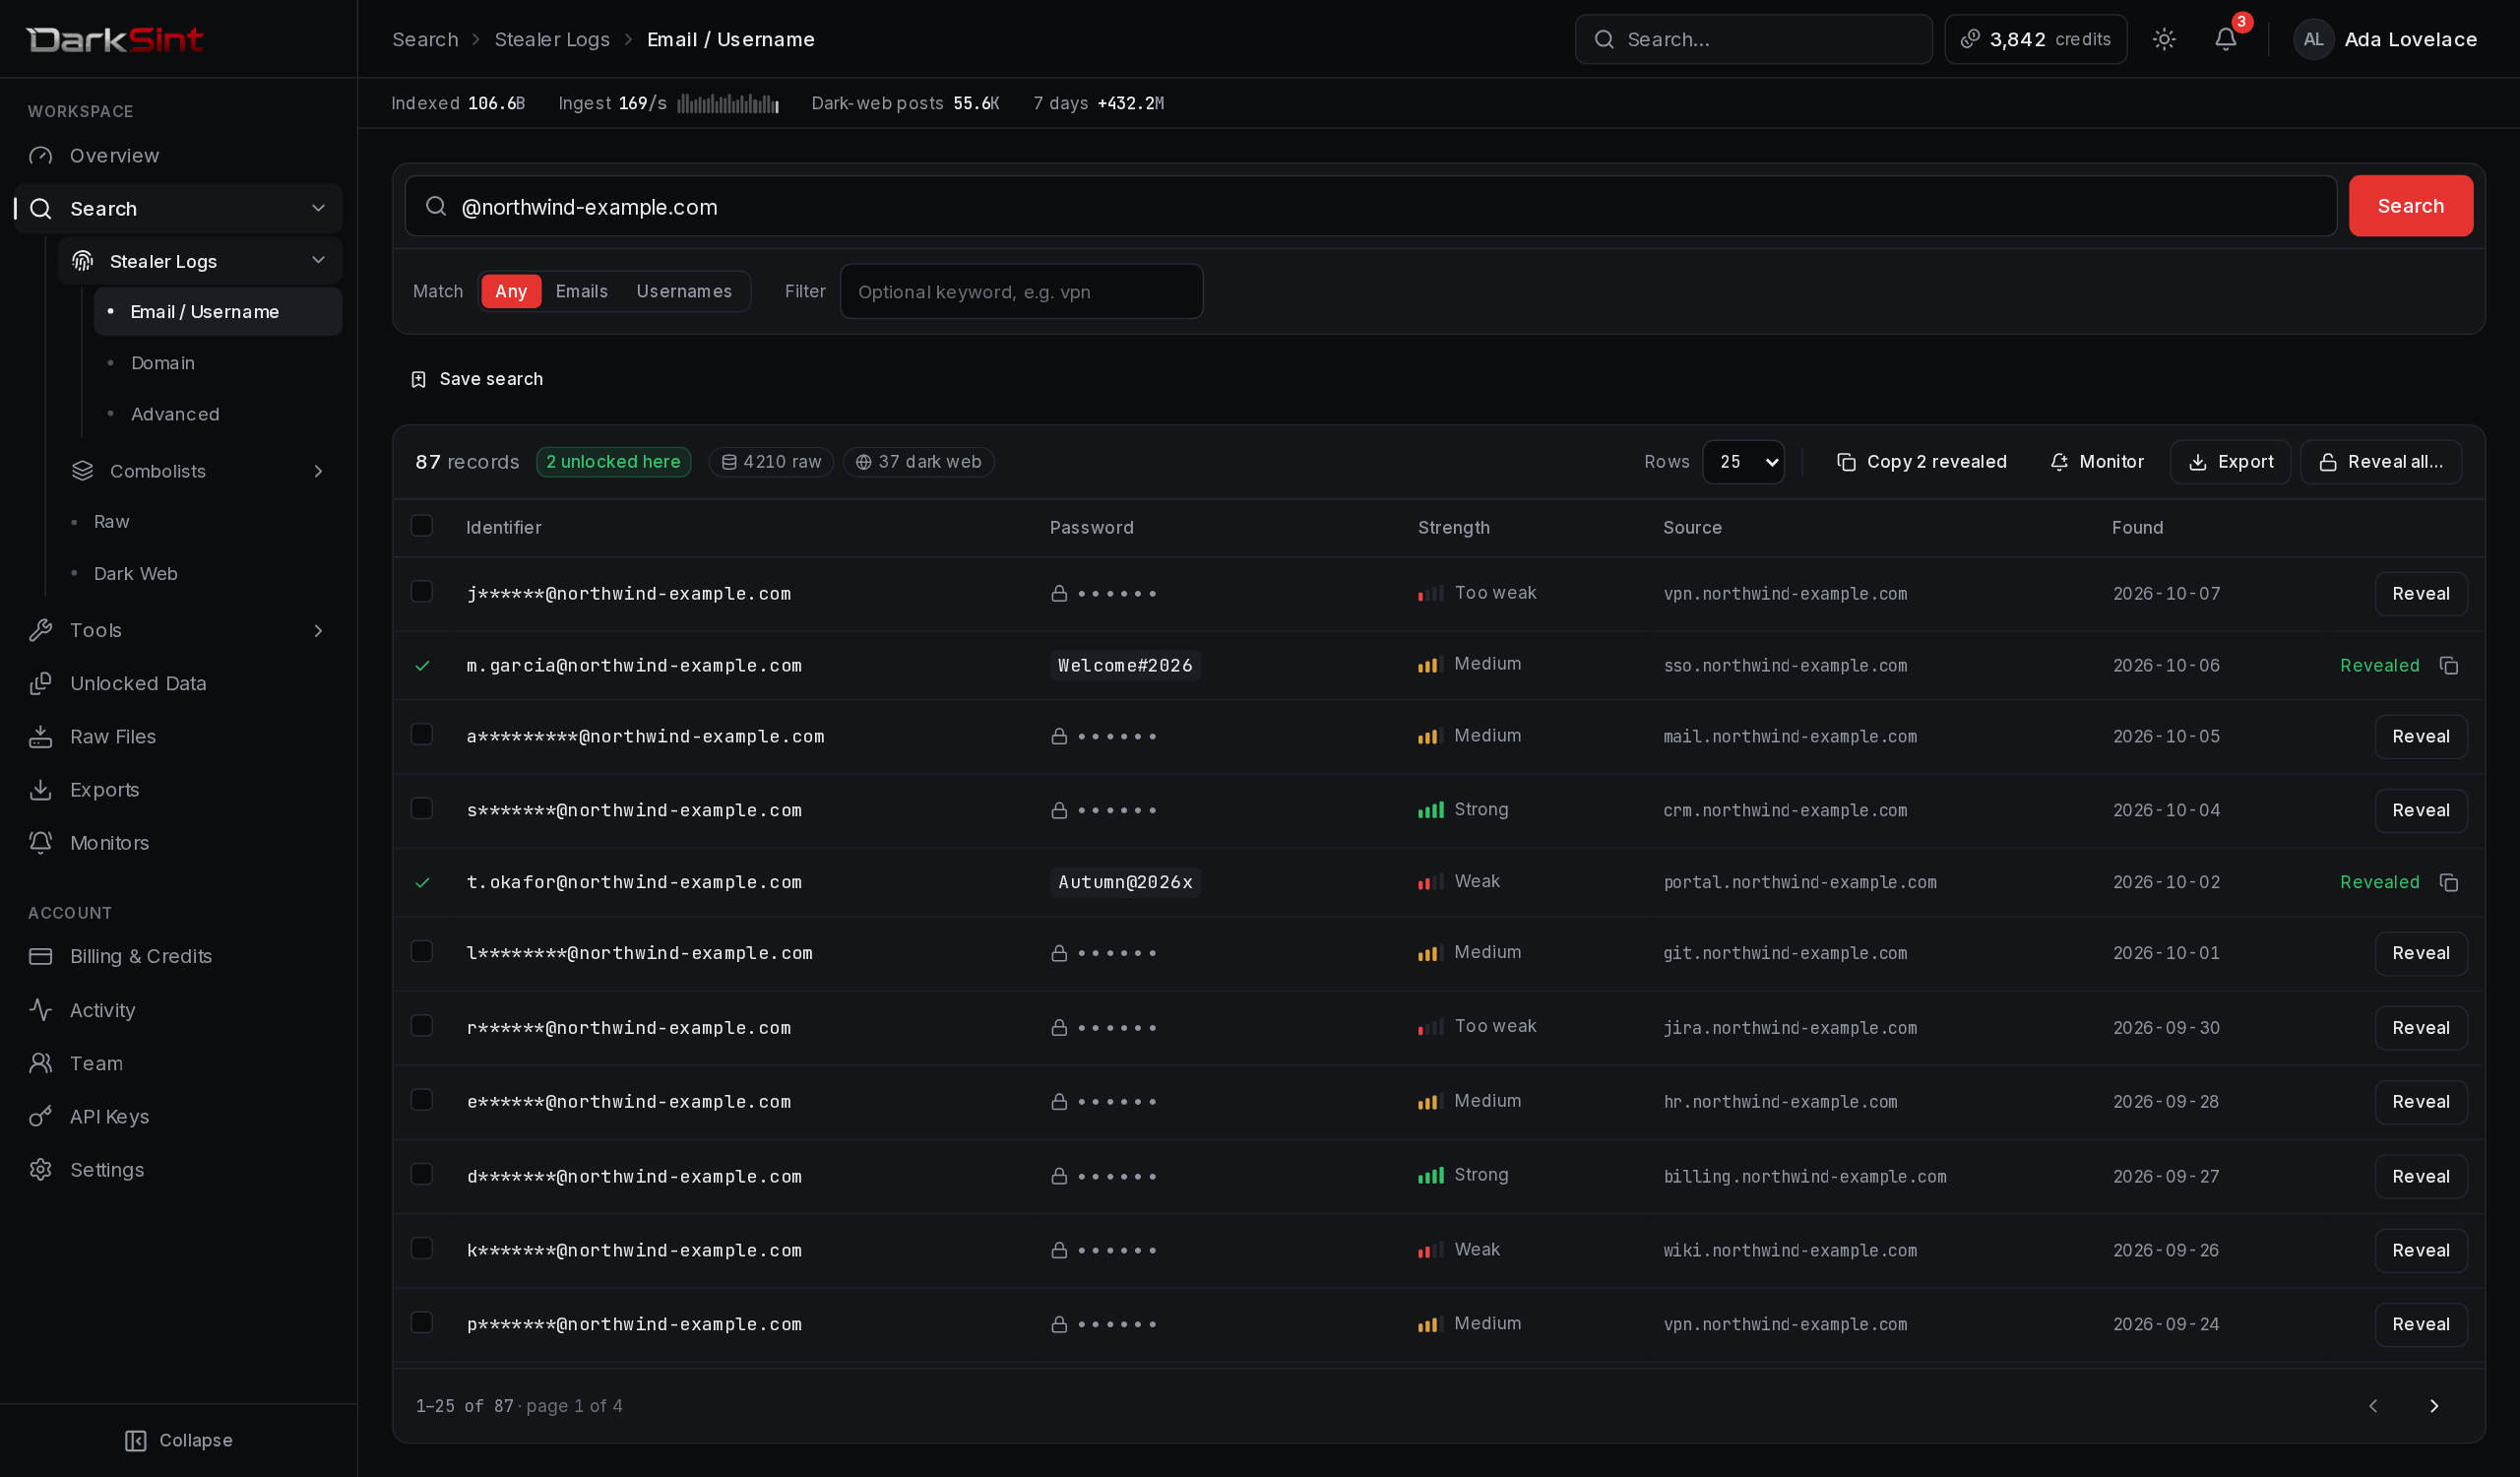
Every identifier, password, and URL arrives redacted. You reveal only what you choose.
One console for the whole exposure surface.
Leaked credentials, dark-web chatter, and raw breach files. Found, revealed, and driven to remediation without leaving a single screen.
Watch the rooms where breaches change hands
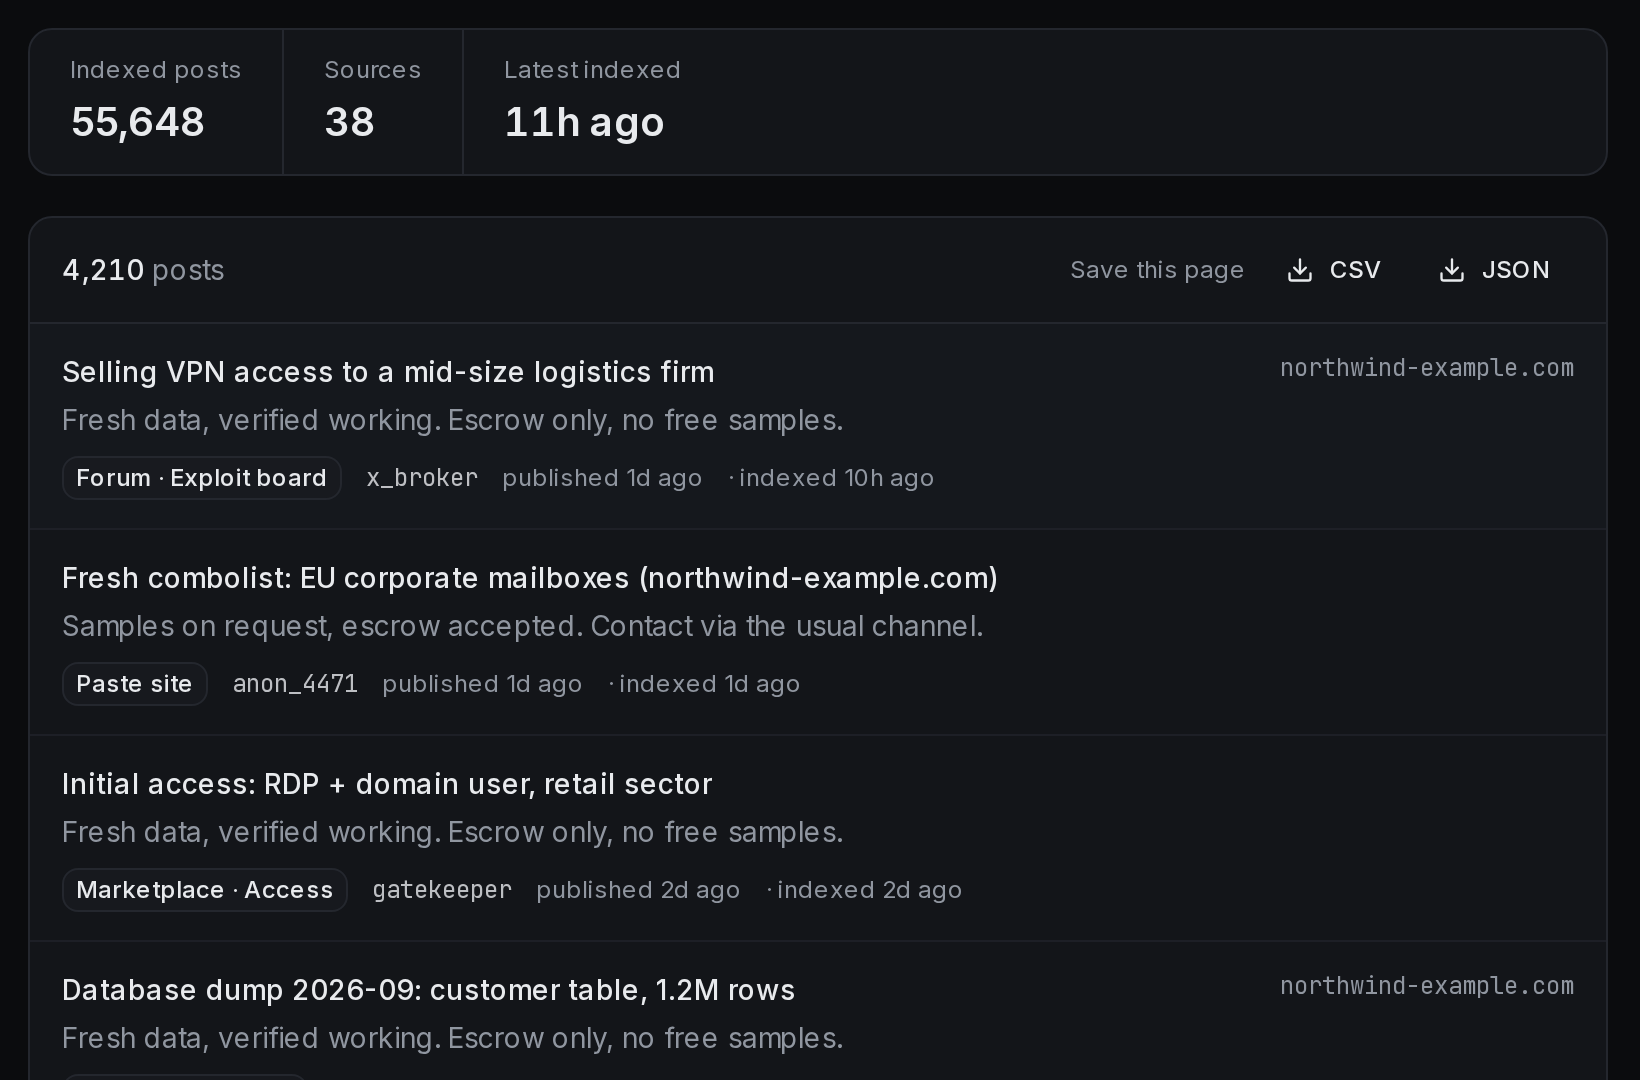
Track your company, domains, and people across the forums and marketplaces where stolen data surfaces first. Read the post, see who wrote it and when, while there's still time to act.
- Filter by source, author, and date
- Read the original next to the redacted view
- Every post attributed to where it came from
Be the first to know, not the last
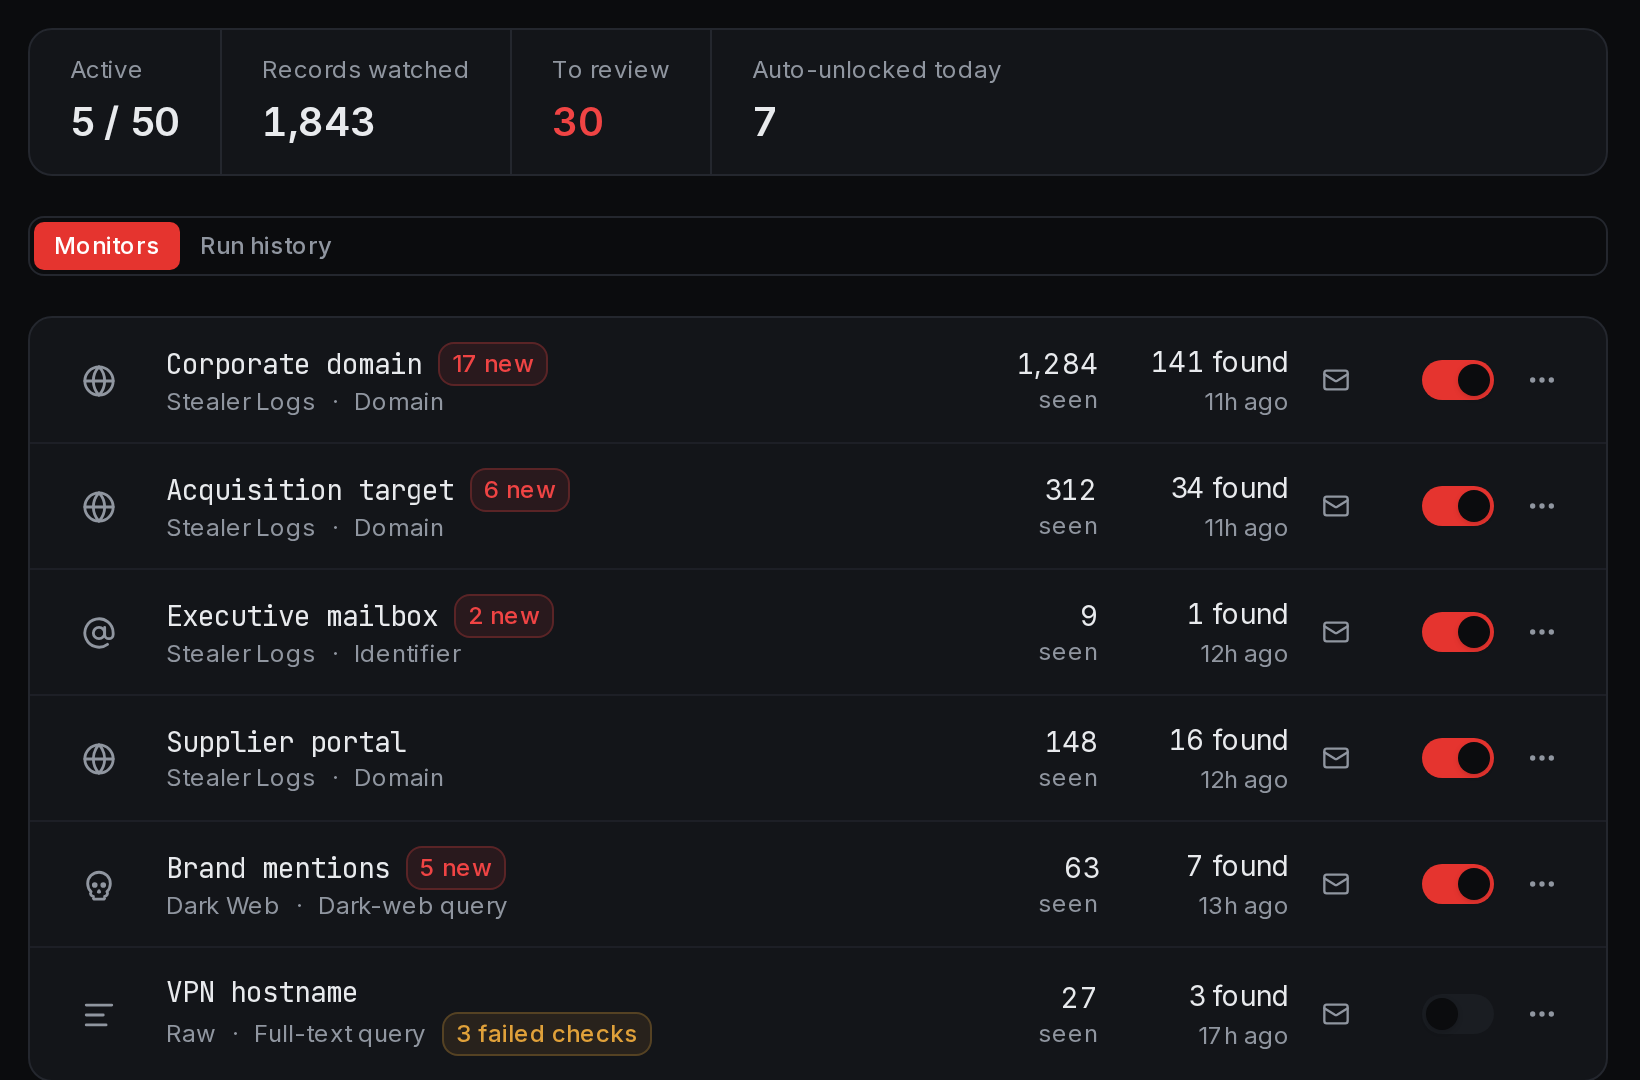
Put a domain or an identifier under watch. The moment new exposure appears, you hear about it: in the app, in your inbox, or straight in your own tooling.
- Alerts by email, Slack, Telegram, Discord, or webhook
- See exactly what's new since the last check
- Every run kept on the record
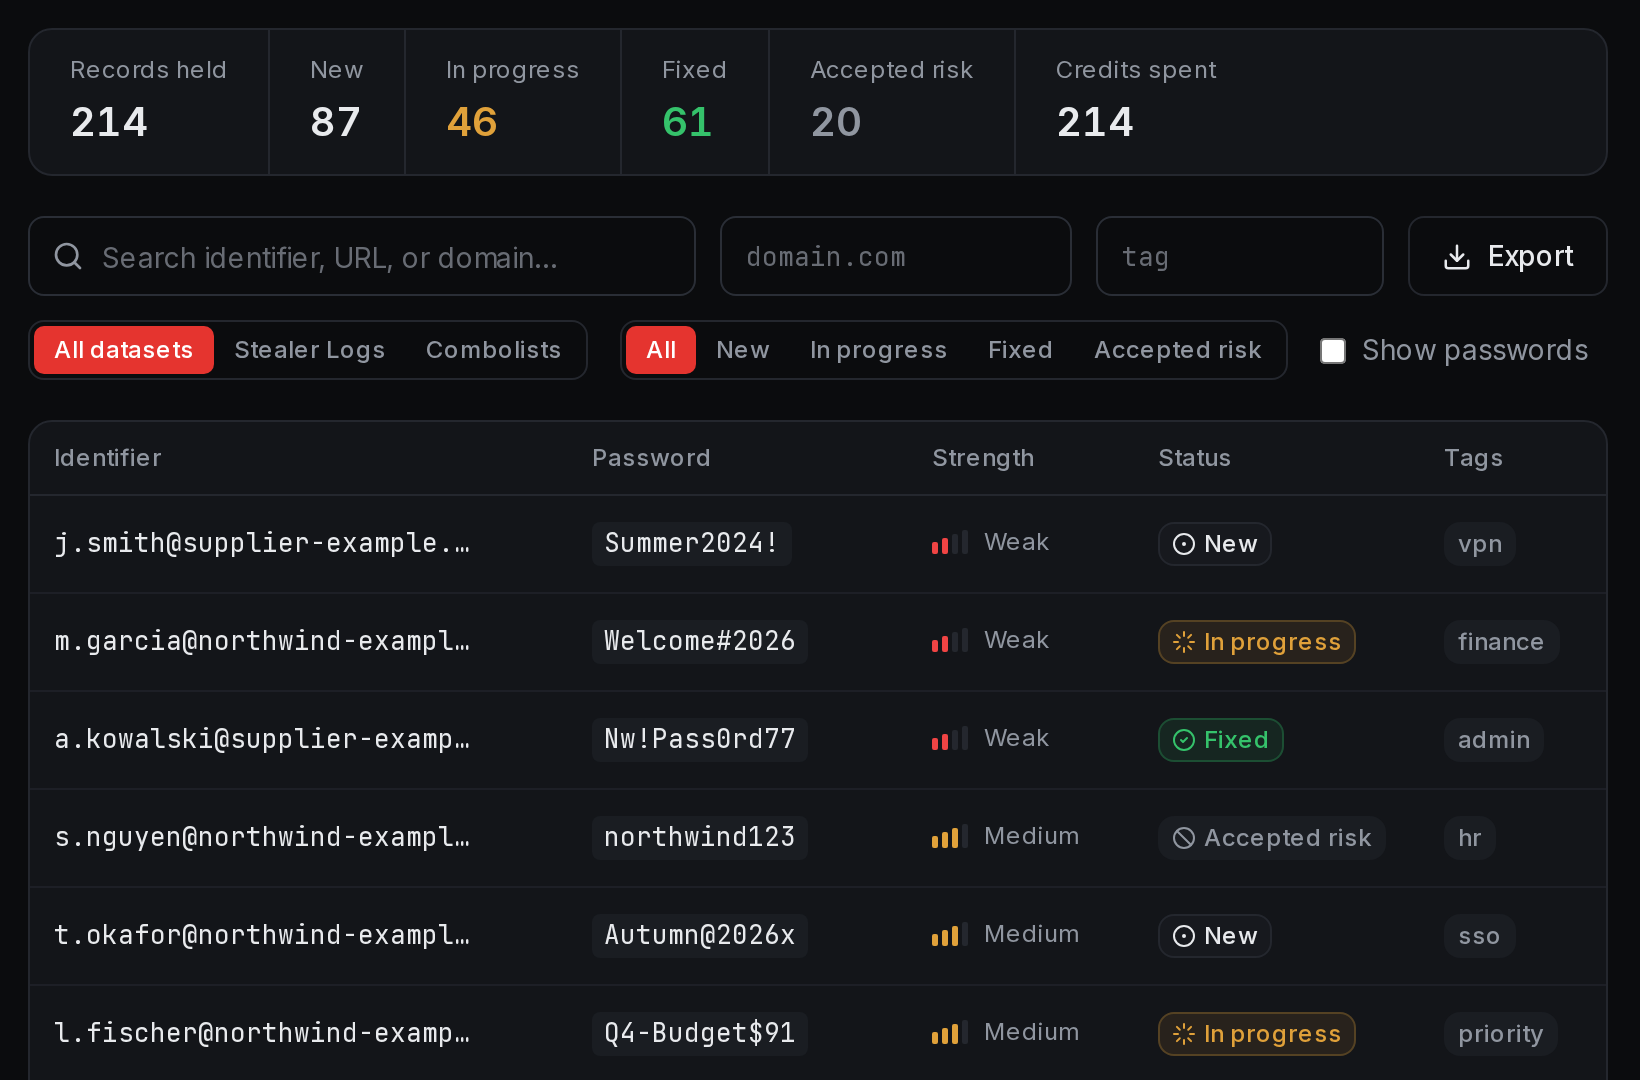
Turn a raw hit into a closed ticket
Everything you reveal becomes yours to work: tag it, note it, and move it from new to fixed. A living record of what you found, and proof of what you did about it.
- Drive each record from new to remediated
- Tag, annotate, and prioritize
- Encrypted, and private to you
Hand the evidence to the room that needs it
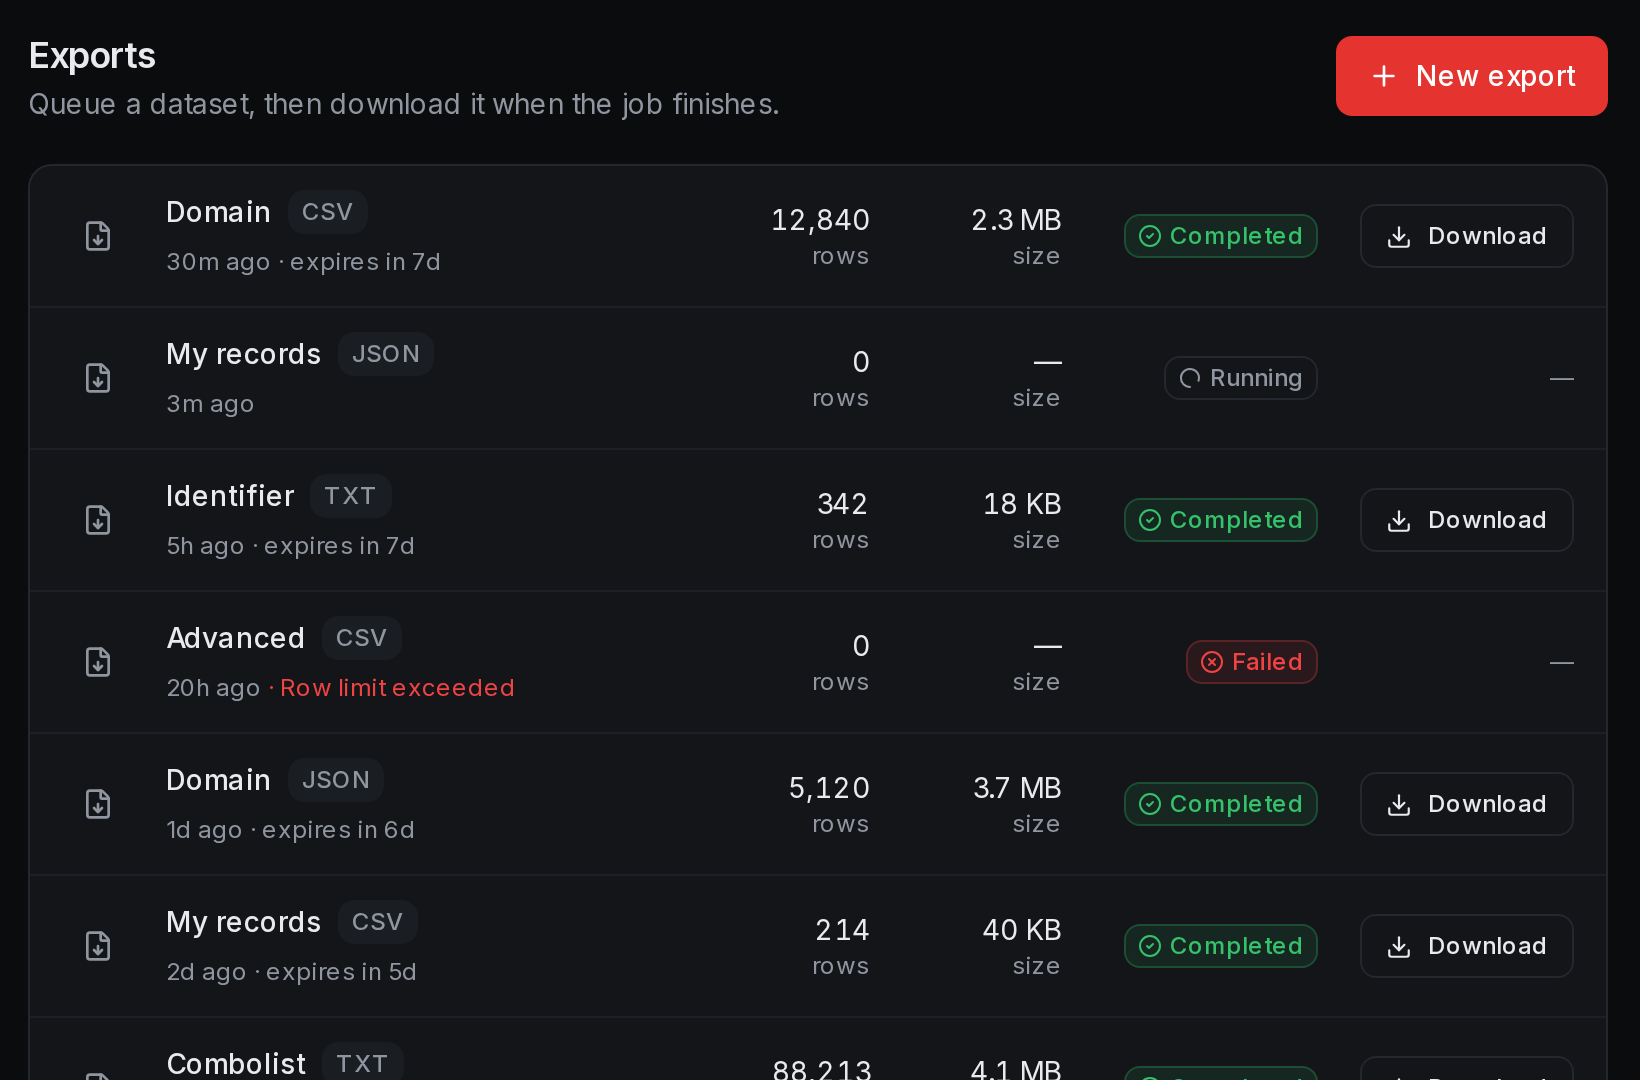
Give a board, an auditor, or an incident playbook exactly what it asks for: a clean pull of a domain, an identifier, or your revealed records, ready the moment you are.
- CSV, JSON, or plain text
- Large pulls prepare in the background
- Private links that expire on their own
From “am I exposed?” to a closed ticket.
The whole loop in one place, and you always know what the next move costs.
Detect
Ask “are we exposed?” across leaked credentials, dark-web posts, and raw breach files from one search bar.
Reveal
See the cost, then unmask only the records that matter. Never more than you asked for.
Remediate
Tag, assign, and drive each record to fixed, with a trail that proves you did.
Monitor
Leave a standing watch, so the next exposure reaches you before it reaches an attacker.
Built for the people who answer “are we exposed?”
One workflow, from a single analyst to a team running exposure for dozens of organisations.
- Security operations and incident response
- Check a domain the moment an incident opens, reveal the accounts that matter, and track each one to fixed, with the history to show what was done.
- MSSPs and security consultants
- Run exposure assessments across client domains, keep a standing monitor on each, and hand over exports that slot straight into the report.
- Penetration testers and red teams
- Scope credential exposure for an authorised engagement, and give the client evidence they can act on rather than a list of guesses.
- Threat intelligence and OSINT analysts
- Follow what is posted on dark-web forums and marketplaces, and pivot from a post to the leaked records behind it in the same console.
DarkSint is for exposure you are entitled to investigate. Read the responsible-use policy.
Credits are money. We treat every spend like it.
Search all day and watch what matters. A credit is spent only when a reveal earns it, and you always see the cost first.
- Pay only to reveal
- Searching and monitoring never cost credits. You spend one only to unmask a record, and the price is on screen before you commit.
- Never charged for nothing
- If a reveal comes back partial, or fails, the credit returns to your balance. You pay for the exposure you actually receive, nothing else.
- Yours alone
- Everything you reveal is encrypted and stays private to you. It is never shown to anyone else who signs into your account.
- Made for teams
- Roles, shared workspaces, and a complete audit trail, so a whole SOC works as one and every action stays on the record.
Built for data this sensitive.
DarkSint handles real, working credentials. The controls around them are specific, and written down.
Read the security overview- Encrypted before storage
- Revealed credentials and two-factor secrets are sealed with AES-256-GCM before they reach the database.
- Hardened accounts
- Argon2id passwords, rotating sessions that revoke on replay, and two-factor on every plan.
- Every action on the record
- Searches and significant actions are logged with time, IP, and request ID, then scrubbed of personal data.
- Honest about the line
- No certification badges we have not earned. What we do not yet claim is published, dated, and plain.
Start free. Scale when the exposure does.
Searching is included on every plan. You spend a credit only when you reveal a record , and you see the cost first.
Free
See whether you are exposed, before you spend anything.
Free forever · no card
No credits
Search and check for free; reveal on a paid plan
- Email, username, and domain search
- Password exposure check, never sent in full
- 20 searches a day
- Results stay masked until you upgrade
Starter
For the analyst working an investigation alone.
500 credits / month
Reveals up to 500 records
…
- Everything in Free
- Advanced, dark-web, and stealer-log search
- 500 searches a day
- 5 monitors with email, Slack, or webhook alerts
- Exports up to 10,000 rows
Professional
For the team that owns detection and response.
5,000 credits / month
Reveals up to 5,000 records
…
- Everything in Starter
- Raw breach-file search and downloads
- API access with personal keys
- Team workspace for up to 5 people
- 50 monitors · 5,000 searches a day
Enterprise
For security organisations and MSSPs running at scale.
Annual agreement
Custom credit volume
Volume pricing per reveal, pooled across your team
- Everything in Professional
- Custom credit volume and shared pools
- Unlimited daily searches
- Larger teams, monitors, and exports
- Priority support and onboarding
See your exposure before someone else does.
Run your first search in under a minute. No card, and nothing is revealed until you decide it should be.